Three regulators can ask about one vendor in the same quarter. A bank examiner wants the due diligence file under the Interagency Guidance. A DFS examiner wants your Part 500 third-party policy. An EU supervisor wants the DORA register of information, in the template, by the deadline. Nothing about the vendor changed. Your paperwork tripled.
Below are the eleven regulations that most often reach a third-party program in financial services, life sciences and aerospace and defense, in that order. Each entry gives you who it applies to, the text that carries the third-party obligation, and what it asks you to get from the vendor. Where a date or status is moving, the entry says what the source said on the day we read it.
None of this is legal advice. Scope turns on charter, license, product class and contract language, so confirm your perimeter with counsel. What this list does is show you where to look and what to ask for.
The Short Answer
Eleven third-party risk regulations shape programs across finance, life sciences and defense: the Interagency Guidance on Third-Party Relationships, the FFIEC IT Examination Handbook, DORA, the EBA outsourcing guidelines, NYDFS Part 500, FDA 21 CFR Part 820, the GxP rules on outsourced activities, HIPAA's business associate provisions, ITAR, CMMC and the DFARS cybersecurity clauses. Every one of them keeps you responsible for what your third parties do.
Why third-party risk management regulations keep multiplying
Same vendor, more regulators
Regulators used to write about outsourcing. Now they write about dependency. In 2023 the US banking agencies named operational, compliance and strategic risk from third parties. DORA put ICT concentration risk and critical providers under direct EU oversight. CMMC pushes one cybersecurity standard down every tier of the defense supply chain. Vocabulary and reach differ, and all of them agree on one point: hiring a third party does not move the obligation.
That is why third party risk management regulations keep landing on the same desk. Each regulator looks at your vendor population through its own lens, cyber for DFS, product quality for FDA, export control for State, and wants evidence in its own format. A program built around one regulator's checklist ends up rebuilding the same vendor file three times.
Certa's overview of the third-party regulatory landscape covers the wider field. These eleven are the ones a regulated enterprise in these three industries gets examined against, grouped by industry and ordered roughly by how often they come up.
Interagency guidance on third-party relationships
The baseline for every US bank
Finalized June 6, 2023, by the Board, FDIC and OCC and published at 88 FR 37920 on June 9, 2023, this guidance "replaces each agency's existing general guidance on this topic and is directed to all banking organizations supervised by the agencies." For OCC third party risk management expectations, the OCC third-party risk management bulletin is the operative document. It rescinds OCC Bulletin 2013-29 and the 2020 FAQs that supplemented it.
Five life cycle stages organize the work: planning, due diligence and third-party selection, contract negotiation, ongoing monitoring and termination, under a governance layer of oversight and accountability, independent reviews, and documentation and reporting. Risk sets the depth. Critical activities, which the guidance characterizes as those that could "cause a banking organization to face significant risk if the third party fails to meet expectations" or "have significant customer impacts," get the most oversight.
- Due diligence evaluates "the volume and types of subcontracted activities and the degree to which the third party relies on subcontractors."
- Documentation includes "a current inventory of all third-party relationships (and, as appropriate to the risk presented, related subcontractors)."
Subcontractors are where most programs fall short. The agencies note in the preamble that the interagency guidance on third-party relationships does not expect a bank to assess every subcontractor of every third party, so write that proportionality into your tiering: critical ones get the look, the rest get the clause.
FFIEC third-party risk management expectations
What the IT examiner brings
Principles come from the Interagency Guidance. Procedures come from the FFIEC IT Examination Handbook, which is what the IT examiner has open during the visit. Its Outsourcing Technology Services booklet, announced in OCC Bulletin 2004-32 on July 15, 2004, puts it plainly: "Outsourcing, however, does not reduce the fundamental risks associated with information technology or the business lines that use it," and oversight "will depend on the criticality of the service, process, or system to the institution's operation."
- Appendix J to the Business Continuity Planning booklet, "Strengthening the Resilience of Outsourced Technology Services" (FDIC FIL-9-2015, February 23, 2015), tests third-party management, third-party capacity, testing with third-party technology service providers, and cyber resilience.
- The Architecture, Infrastructure, and Operations booklet (OCC Bulletin 2021-30, June 30, 2021) replaced the July 2004 Operations booklet and carries sections on oversight of third-party service providers and on shadow IT.
- A February 2026 update, per the InfoBase notice read October 23, 2026, removed references to reputational risk consistent with Executive Order 14331 and creates no new requirements.
For ffiec third party risk management work, map each booklet section to evidence you already hold: the board-approved outsourcing policy, the resilience tests run with each technology service provider, and the inventory that shows no shadow IT.
DORA regulation for ICT third-party providers
A register, a contract standard & an overseer
Regulation (EU) 2022/2554 of 14 December 2022, the Digital Operational Resilience Act, "shall apply from 17 January 2025" under Article 64. Article 2 lists twenty categories of financial entities, from credit institutions and payment institutions through investment firms, insurers, pension institutions and trading venues, then adds a twenty-first: ICT third-party service providers themselves. Article 28(1)(a) sets the premise. Financial entities using ICT services "shall, at all times, remain fully responsible for compliance with, and the discharge of, all obligations under this Regulation."
- Article 28(3): a "register of information in relation to all contractual arrangements on the use of ICT services provided by ICT third-party service providers," separating those that support critical or important functions, reported on yearly and produced in full on request.
- Article 28(4): a pre-contract assessment of criticality, due diligence, conflicts of interest and ICT concentration risk under Article 29.
- Article 30(2): every ICT contract states whether subcontracting a service that supports a critical or important function "is permitted and, when that is the case, the conditions applying to such subcontracting," plus where the service runs and the data lives.
- Article 30(3): for critical or important functions, full service level descriptions, notice periods, tested contingency plans, threat-led penetration testing, "unrestricted rights of access, inspection and audit," and exit strategies.
Article 31 adds the piece no earlier outsourcing rule had. The European Supervisory Authorities can designate ICT third-party providers as critical and appoint a Lead Overseer for each, so your cloud provider may have its own supervisor.
Under the dora regulation the register is the first thing a supervisor asks for, and the one most programs cannot produce from a spreadsheet. Nikki Stoy walks through the operational side in Certa's DORA compliance challenges podcast.
EBA outsourcing guidelines for EU banks
The outsourcing rulebook, successor pending
Before DORA there were the eba outsourcing guidelines, EBA/GL/2019/02, published February 25, 2019. They apply "from 30 September 2019 to all outsourcing arrangements entered into, reviewed or amended on or after this date," with existing arrangements documented by December 31, 2021. They repealed the 2006 CEBS outsourcing guidelines and the EBA's 2017 cloud recommendations, and they still govern the non-ICT outsourcing DORA does not reach. Anyone who has built a DORA register will recognize the structure, because DORA borrowed it.
- Section 4 defines critical or important functions and applies stricter requirements when they are outsourced.
- Section 11 requires a register of all outsourcing arrangements.
- Section 12 covers pre-outsourcing analysis, risk assessment and due diligence.
- Section 13.1 governs sub-outsourcing of critical or important functions, which "requires ex ante notification" to the institution.
- Section 15 requires exit strategies, including "a documented exit plan for each critical or important function to be outsourced."
Status is in motion. On October 23, 2026, the EBA's page for these guidelines showed a successor, the "Guidelines on the sound management of third-party risk related to non-ICT services," marked "Final and awaiting translation into the EU official languages" and "Not yet applicable," with a press release dated 18 September 2026 and no application date filled in. Once applicable, the page says, the new guidelines will repeal the Guidelines on outsourcing arrangements. Until then, EBA/GL/2019/02 is the text your supervisor is reading.
NYDFS cybersecurity rules for third-party service providers
Four things your vendor policy must address
New York's cybersecurity regulation took effect March 1, 2017, and its second amendment took effect November 1, 2023. Section 500.1 defines a third-party service provider as a person that is not an affiliate or a governmental entity, provides services to the covered entity, and "maintains, processes or otherwise is permitted access to nonpublic information through its provision of services." That definition fixes the population your policy must cover. Section 500.11(a) then requires written policies and procedures, based on your risk assessment, addressing four things:
- "the identification and risk assessment of third-party service providers"
- the "minimum cybersecurity practices required to be met" by them to do business with you
- the due diligence used to evaluate the adequacy of those practices
- "periodic assessment of such third-party service providers based on the risk they present and the continued adequacy of their cybersecurity practices"
Section 500.11(b) adds guidelines on each provider's access controls, including multi-factor authentication under 500.12, its encryption under 500.15, and the notice it owes you after a cybersecurity event.
What makes nydfs part 500 different is the clock in 500.17(a)(1): notice to the superintendent "as promptly as possible but in no event later than 72 hours after determining that a cybersecurity incident has occurred at the covered entity, its affiliates, or a third-party service provider." Your vendor contract's notification window has to leave room to meet that.
FDA quality system rules for suppliers
The QMSR made supplier audits inspectable
FDA's final rule "Medical Devices; Quality System Regulation Amendments" was published February 2, 2024, at 89 FR 7496 and became effective February 2, 2026. It rewrote 21 cfr 820 into the Quality Management System Regulation by incorporating ISO 13485:2016 by reference. Under 820.10(a) a manufacturer must "document a quality management system that complies with the applicable requirements of ISO 13485." Scope stays on finished devices, and 820.1(a) names the contractors it covers, including those performing "contract sterilization, installation, relabeling, remanufacturing, repacking, or specification development." Component makers sit outside it, though FDA encourages them to follow the rule.
For third-party risk the biggest change is visibility. FDA's QMSR FAQ, updated February 2, 2026, says the QMSR "gives the FDA the authority to inspect management review, quality audits, and supplier audit reports," and that the exceptions that existed at 820.180(c) "are not maintained in the QMSR." On the same date FDA stopped using QSIT and began inspecting under Compliance Program 7382.850. Supplier audit reports written for internal eyes are now exam evidence.
So your supplier qualification, evaluation criteria and re-evaluation records need to read like ISO 13485 purchasing controls, with the risk rationale for each supplier's control level in the file, not in someone's head.
GxP compliance for suppliers & contract manufacturers
The contract giver stays responsible
GxP is the family name for good manufacturing, clinical, laboratory and distribution practice, and on outsourcing the texts speak with one voice. EU GMP Chapter 7, "Outsourced Activities," revised in view of ICH Q10 with a deadline for coming into operation of January 31, 2013, opens with the principle that any outsourced GMP activity "should be appropriately defined, agreed and controlled" under a written contract between Contract Giver and Contract Acceptor. Paragraph 7.4 leaves no gap: the Contract Giver "is ultimately responsible to ensure processes are in place to assure the control of outsourced activities."
Read in order, the chapter is a third-party lifecycle:
- Before outsourcing, assess "the legality, suitability and the competence of the Contract Acceptor" (7.5).
- During the relationship, "monitor and review the performance of the Contract Acceptor" (7.7) and review its records and results (7.8).
- On fourth parties, the Contract Acceptor "should not subcontract to a third party any of the work entrusted to him under the Contract without the Contract Giver's prior evaluation and approval" (7.11).
- Expect inspection: outsourced activities "may be subject to inspection by the competent authorities" (7.13).
US drug CGMPs land in the same place. Under 21 CFR 211.22(a), the quality control unit "shall be responsible for approving or rejecting drug products manufactured, processed, packed, or held under contract by another company," and under 211.84(d)(2) a supplier's report of analysis can replace your own testing only with an identity test and "appropriate validation of the supplier's test results at appropriate intervals." That validation cadence is a gxp compliance obligation that belongs in the supplier file as much as in the lab. Certa for life sciences lists the frameworks Certa covers for CROs, CMOs and distributors, from FDA 21 CFR and GMP through GCP oversight and HIPAA.
HIPAA business associate requirements
Assurances, in writing, down the chain
HIPAA's third-party rule is the business associate agreement. Under 45 CFR 164.502(e)(1)(i), a covered entity may let a business associate handle protected health information only "if the covered entity obtains satisfactory assurance that the business associate will appropriately safeguard the information," documented in a written contract under 164.502(e)(2). Down one tier, 164.502(e)(1)(ii) requires a business associate to obtain the same assurances from any subcontractor it uses. Section 164.504(e)(2) lists what the contract must say. Among the terms the business associate must accept:
- Report any use or disclosure not provided for by the contract, "including breaches of unsecured protected health information as required by § 164.410," which 164.410(b) sets at "without unreasonable delay and in no case later than 60 calendar days after discovery of a breach."
- Ensure subcontractors "agree to the same restrictions and conditions that apply to the business associate."
- Make its books and records available to the Secretary, and at termination return or destroy the information where feasible.
A monitoring duty hides in 164.504(e)(1)(ii). A covered entity is out of compliance if it "knew of a pattern of activity or practice of the business associate that constituted a material breach or violation" and did not take reasonable steps to cure it, then terminate if those steps failed and termination was feasible. Knowing and not acting is the violation. Log it like one.
ITAR compliance for defense exporters
Registration first, then every release
22 CFR Parts 120 through 130 implement section 38 of the Arms Export Control Act (22 U.S.C. 2778) and are administered by the State Department's Directorate of Defense Trade Controls. A defense article under 120.31 is any item or technical data on the United States Munitions List in 121.1, including unfinished forgings and castings once they are identifiable as defense articles. Export under 120.50 covers more than shipping. It includes "releasing or otherwise transferring technical data to a foreign person in the United States (a deemed export)" and performing a defense service for a foreign person anywhere.
Registration is the third-party hook. Section 122.1(a) requires "any person who engages in the United States in the business of manufacturing or exporting or temporarily importing defense articles, or furnishing defense services" to register with DDTC, and "a manufacturer who does not engage in exporting must nevertheless register." One occasion counts. A machine shop three tiers down that cuts a USML part is in scope whether or not it knows it. Penalties explain why itar compliance is a procurement question: 127.7 provides for administrative debarment, "generally" for three years, and 127.10, as the eCFR read on October 23, 2026, sets the civil penalty per violation of 22 U.S.C. 2778 at up to the greater of $1,271,078 "or the amount that is twice the value of the transaction."
- DDTC registration status for every supplier that will manufacture or handle a defense article.
- Foreign ownership, control and the nationality of personnel with access to technical data.
- The license, agreement or exemption a planned release would rely on, recorded before the drawing goes out.
CMMC compliance across the defense supply chain
One standard, every tier, by phase
Published October 15, 2024, at 89 FR 83092 and effective December 16, 2024, 32 CFR Part 170 applies to "all DoD contract and subcontract awardees that will process, store, or transmit information, in performance of the DoD contract, that meets the standards for FCI or CUI on contractor information systems." Four statuses exist: Level 1 (Self), Level 2 (Self), Level 2 (C3PAO), assessed by a certified third-party assessment organization, and Level 3 (DIBCAC), assessed by DCMA. Section 170.23 turns cmmc compliance into a supplier management program. Requirements "apply to prime contractors and subcontractors throughout the supply chain at all tiers":
- A subcontractor handling only FCI needs Level 1 (Self).
- A subcontractor handling CUI needs at least Level 2 (Self).
- Level 2 (C3PAO) is the minimum when the prime contract requires Level 2 (C3PAO) or Level 3 (DIBCAC).
DoD's DFARS rule, published September 10, 2025, at 90 FR 43560 and effective November 10, 2025, carries this into clause 252.204-7021: flow down the correct level, keep CUI off systems without the required status, and "ensure all subcontractors and suppliers complete prior to subcontract award, and maintain on an annual basis, an affirmation" of continuous compliance in SPRS. Rollout is phased under 170.3(e):
- Phase 1 began on the DFARS rule's effective date, November 10, 2025, with Level 1 (Self) or Level 2 (Self) as a condition of award.
- Phase 2 begins one calendar year later and adds Level 2 (C3PAO). As of October 23, 2026, that puts it at November 10, 2026.
- Phase 3 begins one calendar year after Phase 2 and adds Level 3 (DIBCAC).
- Phase 4, full implementation, follows one year after that. DFARS 204.7504 matches it: on or after November 10, 2028, the clause applies whenever contractor systems will handle FCI or CUI.
One operational note from the DFARS preamble: there is no automated way for a prime to view a subcontractor's status in SPRS, so subcontractors share their own record and the prime keeps the evidence. Certa for aerospace & defense lists CMMC, NIST SP 800-171 and DFARS among the frameworks Certa covers for A&D supply chains.
DFARS compliance & contract flow-downs
The clauses already in your contracts
CMMC did not replace the DFARS cybersecurity clauses. It sits on top of them, and for most primes they are the gate a supplier meets first:
- 252.204-7012 requires covered contractor information systems to meet "the security requirements in National Institute of Standards and Technology (NIST) Special Publication (SP) 800-171," requires cyber incidents to be rapidly reported to DoD, defined as within 72 hours of discovery, and under paragraph (m) flows to subcontracts "without alteration, except to identify the parties."
- 252.204-7019 makes award conditional on "a current assessment (i.e., not more than 3 years old unless a lesser time is specified in the solicitation)" with summary level scores posted in the Supplier Performance Risk System.
- 252.204-7020(g) carries that down a tier: the contractor "shall not award a subcontract or other contractual instrument" unless the subcontractor has completed, within the last three years, at least a Basic NIST SP 800-171 DoD Assessment.
So dfars compliance for a prime is a before-award gate with three checks per supplier: the 7012 clause flowed down verbatim, a current SPRS score, and, as CMMC phases in, the status and affirmation 7021 requires.
Build those into supplier onboarding with dates attached. Every one of them expires.
Meeting overlapping regulations with Certa
One third-party record, eleven answers
Read the eleven entries again and the asks repeat. An inventory or register. Risk-based due diligence with the rationale kept. Contract terms that carry the obligation down a tier. Monitoring between assessments. Notice windows measured in hours. A program that answers those once, and maps each regulator's question to the same record, stops rebuilding the vendor file per regulator.
That is how Certa's Third Party OS is built. Certa's industry pages list the coverage by vertical: for financial services, the OCC, FDIC and FRB Interagency Guidance, DORA, NYDFS, FCPA, AML and fourth-party and concentration risk. For life sciences, FDA 21 CFR, FDASIA, GMP and ISO 9001, HIPAA and HITECH, ABAC, GCP clinical trials oversight, supply chain integrity and responsible sourcing. For aerospace and defense, CMMC, NIST SP 800-171 and DFARS, ITAR and EAR, sanctions and denied party screening, n-tier visibility and FOCI, with documentation Certa describes as holding up "under DCMA, DCAA, and regulatory scrutiny." This table maps each regulation in the list to the Certa capability that supports it, using only what Certa's own site describes.
| Regulation | What it asks of your program | Certa capability |
|---|---|---|
| Interagency Guidance | Risk-based lifecycle, current inventory, documentation | Intake to offboarding on one platform, every third party scored across seven risk domains, risk-tiered due diligence |
| FFIEC IT Handbook | Oversight of technology service providers, tested resilience | Operational and resilience and infosec and cyber domains, with live feeds from BitSight, Black Kite, Rapid Ratings and Interos |
| DORA | Register of information, mandatory contract terms, exit strategies | One register of third parties and contracts, Contracts Agent flagging missing or non-standard clauses, obligations, SLAs and key dates, offboarding that closes out access and data |
| EBA outsourcing guidelines | Register of outsourcing, exit plans for critical functions | The same register and tiering, with periodic assessment tuned to each vendor's risk tier |
| NYDFS Part 500 | Identify, set minimum practices, vet, reassess periodically | Risk Agent for InfoSec risk assessments that surfaces only what needs your review, continuous monitoring and alerting |
| FDA QMSR (21 CFR 820) | Supplier controls to ISO 13485, supplier audits inspectable | Supplier onboarding and periodic assessment with an audit trail of documented rationale, citations and timestamps, exportable on demand |
| GxP (EU GMP Ch. 7, 21 CFR 211) | Assess, approve subcontracting, review records | Pre-Fill Agent that pre-populates DDQs from supplier documents and websites, remediation tasks with tracked evidence, sub-tier visibility |
| HIPAA | Written assurances down the chain, act on known patterns | Contracts Agent for required terms and obligations, alerting on changes, a disposition log for every decision |
| ITAR | Registration, ownership and authorizations before release | Sanctions, denied party and UBO screening, with the Adjudicate Agent's confidence-scored, explainable calls on hits |
| CMMC | Status and affirmation from every subcontractor before award | Cyber Security Cert. (CMMC) Agent and n-tier supply chain visibility |
| DFARS 7012, 7019, 7020 | Clause flowdown, SPRS scores, 72-hour reporting | Contracts Agent tracking obligations and key dates, Vibe Configuration™ to turn a new clause into a live workflow with no code |
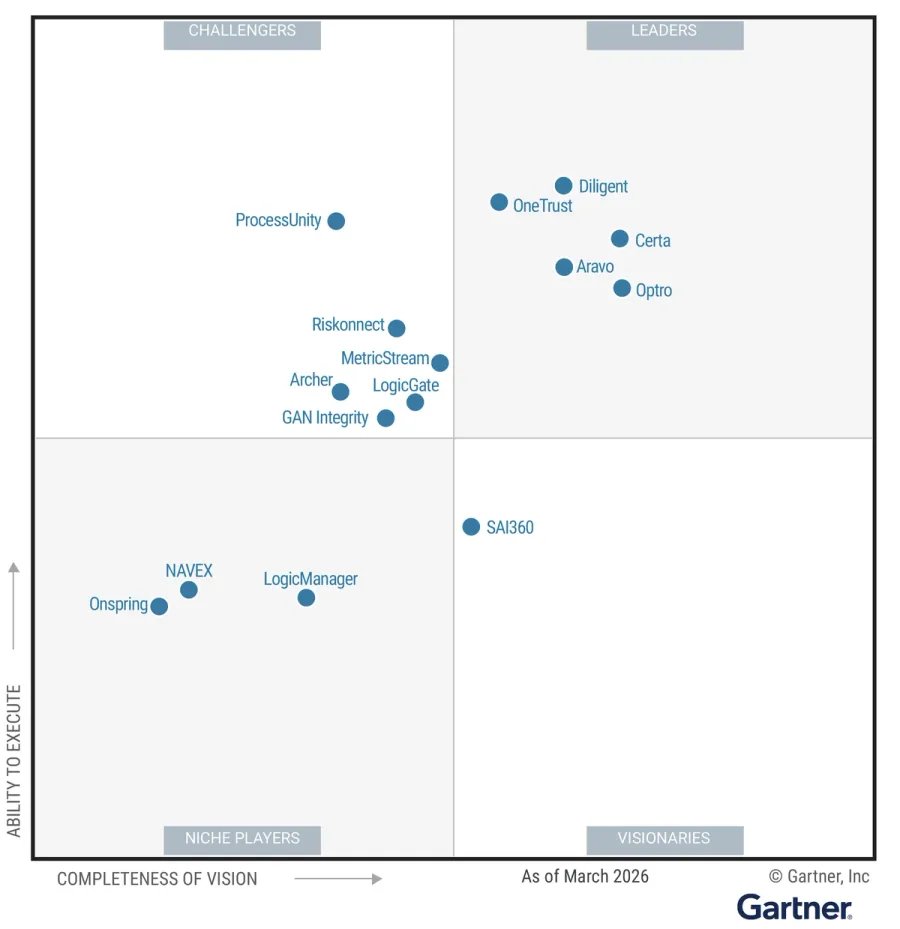
Two outcomes from Certa's site show what that looks like under scrutiny. A top 5 EU financial institution cut vendor onboarding from 10 weeks to 1 day. A global life sciences leader with more than 50,000 third parties automated 1,000+ monthly third-party requests through Data Agent DDQ pre-fill across 20 risk domains. Certa was named a Leader in the 2026 Gartner® Magic Quadrant™ for Third-Party Risk Management Tools for Assurance Leaders.
Sources
- OCC Bulletin 2023-17, Third-Party Relationships: Interagency Guidance on Risk Management (June 6, 2023)
- Federal Register, Interagency Guidance on Third-Party Relationships: Risk Management, 88 FR 37920 (June 9, 2023)
- OCC Bulletin 2004-32, FFIEC IT Booklets on Outsourcing Technology Services and Management (July 15, 2004)
- FFIEC IT Examination Handbook, Outsourcing Technology Services booklet
- FDIC FIL-9-2015, Business Continuity Planning Booklet Appendix J Update (February 23, 2015)
- OCC Bulletin 2021-30, FFIEC IT Examination Handbook: New Architecture, Infrastructure, and Operations Booklet (June 30, 2021)
- FFIEC IT Examination Handbook, Architecture, Infrastructure, and Operations booklet
- EUR-Lex, Regulation (EU) 2022/2554 (DORA), Articles 2, 28 to 31 and 64
- EBA, Final Report on EBA Guidelines on outsourcing arrangements, EBA/GL/2019/02 (February 25, 2019)
- EBA, Guidelines on outsourcing arrangements page, including the successor guidelines on third-party risk related to non-ICT services (read October 23, 2026)
- NYDFS, 23 NYCRR Part 500 as amended November 1, 2023, sections 500.1, 500.11, 500.17 and 500.22
- Federal Register, Medical Devices; Quality System Regulation Amendments, 89 FR 7496 (February 2, 2024)
- FDA, Quality Management System Regulation, Frequently Asked Questions (updated February 2, 2026)
- eCFR, 21 CFR Part 820, Quality Management System Regulation
- eCFR, 21 CFR Part 211, sections 211.22 and 211.84
- European Commission, EudraLex Volume 4, EU GMP Chapter 7, Outsourced Activities (in operation January 31, 2013)
- eCFR, 45 CFR 164.502, Uses and disclosures of protected health information: general rules
- eCFR, 45 CFR 164.504, Uses and disclosures: organizational requirements
- eCFR, 45 CFR 164.410, Notification by a business associate
- eCFR, 22 CFR Subchapter M, International Traffic in Arms Regulations, Parts 120 to 130
- eCFR, 32 CFR Part 170, Cybersecurity Maturity Model Certification Program
- Federal Register, Cybersecurity Maturity Model Certification (CMMC) Program, 89 FR 83092 (October 15, 2024)
- Federal Register, DFARS: Assessing Contractor Implementation of Cybersecurity Requirements, 90 FR 43560 (September 10, 2025)
- Acquisition.gov, DFARS 252.204-7012 Safeguarding Covered Defense Information and Cyber Incident Reporting
- Acquisition.gov, DFARS 252.204-7019 Notice of NIST SP 800-171 DoD Assessment Requirements
- Acquisition.gov, DFARS 252.204-7020 NIST SP 800-171 DoD Assessment Requirements
- Acquisition.gov, DFARS 252.204-7021 Contractor Compliance With the Cybersecurity Maturity Model Certification Level Requirements
Third-party regulation questions & answers
Short answers to the scoping questions that come up once a program starts mapping regulations to vendors.
Which Third-Party Risk Regulations Apply to Banks?
Every US banking organization supervised by the Federal Reserve, FDIC or OCC falls under the 2023 Interagency Guidance on Third-Party Relationships, and its IT outsourcing is examined against the FFIEC IT Examination Handbook. Institutions regulated by the New York Department of Financial Services add 23 NYCRR 500.11. EU credit institutions and the EU arms of global banks add DORA for ICT services and EBA/GL/2019/02 for other outsourcing. Which combination applies depends on charter, licenses and where the entity is authorized, so map the perimeter with counsel.
Does DORA Apply to US Companies?
Not because of where they are based, but often because of whom they serve. Article 2 of Regulation (EU) 2022/2554 applies to twenty categories of EU financial entities and to ICT third-party service providers. A US firm that provides ICT services to an in-scope EU entity will see Article 30's contract terms in its agreements, and one that the European Supervisory Authorities designate as critical under Article 31 comes under a Lead Overseer. A US group with an EU-authorized subsidiary is in scope through that entity.
Do Life Sciences Companies Need a TPRM Program?
In effect, yes, even though the rules never use the term. Under 21 CFR 211.22(a) the quality control unit approves or rejects product made under contract by another company. EU GMP Chapter 7 makes the Contract Giver ultimately responsible for controlling outsourced activities and requires approval of any subcontracting. The QMSR, effective February 2, 2026, makes supplier audit reports inspectable. HIPAA adds business associate agreements for any partner touching protected health information. A program that tiers, assesses and monitors those relationships is how a company meets all four at once.
What Happens If a Subcontractor Fails CMMC?
The prime cannot flow that work to it. Under 32 CFR 170.23 and DFARS 252.204-7021(f)(2), before awarding a subcontract the contractor must ensure the subcontractor has a current CMMC status at the level appropriate for the information being flowed down, and the DFARS rule's preamble says primes are not to disseminate FCI or CUI to subcontractors that have not indicated they meet that level. A subcontractor with a Conditional status has a plan of action and milestones to close out, within 180 days under the clause's definition of current, before it reaches Final. Until then the prime either holds the controlled information or finds another source.
Compliance Articles
Keep reading